
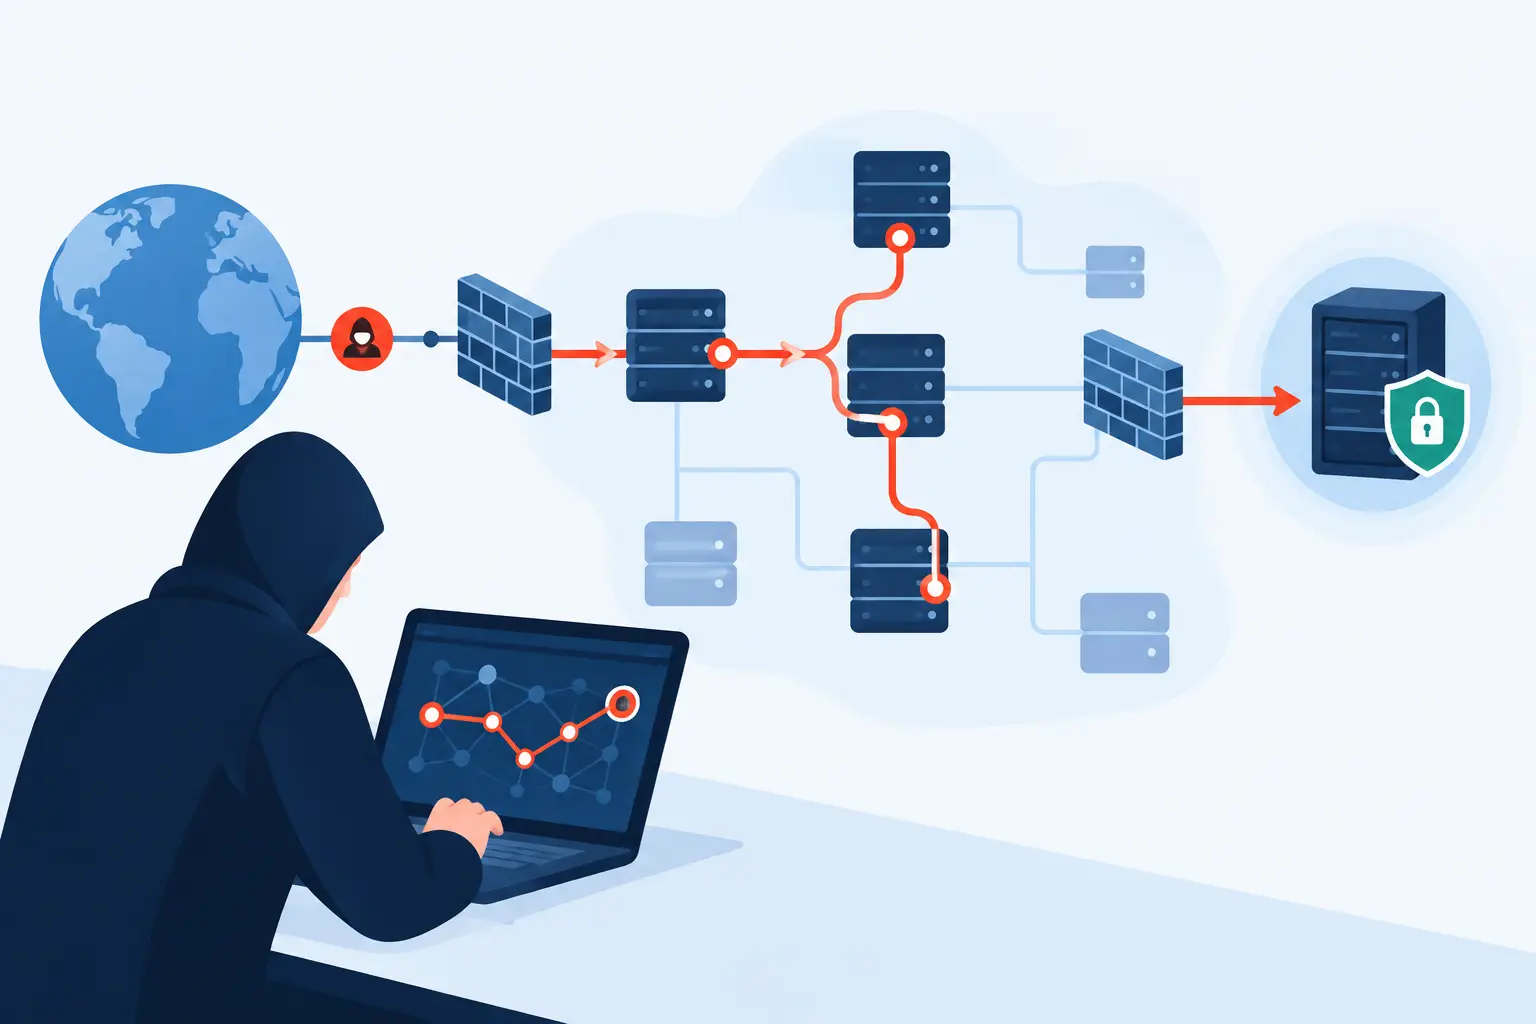
A public-facing asset can look clean on a vulnerability dashboard and still offer an attacker a route into the business. A forgotten subdomain, exposed remote service, weak authentication flow or misconfigured cloud application may only become dangerous when the weaknesses are chained together. That is the value of external penetration testing: it tests the organisation as an adversary would see it, not simply as an asset inventory sees it.
For security leaders, the outcome should not be another long list of findings. It should be a clear view of which external exposures create a credible path to business impact, what needs fixing first and whether the controls already in place can detect or stop real attack activity.
What external penetration testing actually tests
External penetration testing is an authorised assessment of systems accessible from the public internet. A skilled tester begins with reconnaissance, building a picture of the organisation’s digital footprint through domains, IP addresses, cloud services, web applications, exposed infrastructure and publicly available information.
The tester then looks for a route in. This can include exploitable vulnerabilities, poor configuration, exposed credentials, insecure application logic, weak access controls and services that should never have been publicly reachable. Where permitted in the engagement scope, they validate whether separate weaknesses can be combined to gain access, escalate privileges or reach sensitive data.
The distinction matters. An external vulnerability scan can report that a server is missing a patch. A penetration test investigates whether that server is reachable, whether the weakness is exploitable in its real configuration and what an attacker could do after gaining a foothold. The scan identifies potential issues. The test establishes attackability and consequence.
Why an attacker-led view changes remediation priorities
Security teams often have more findings than they can realistically address in a quarter. Severity scores help, but they are not a complete prioritisation model. A critical vulnerability on an isolated system may create less immediate risk than a medium-rated weakness on an internet-facing application that can be chained with a misconfiguration and an over-privileged account.
External penetration testing puts context around those decisions. It asks whether the asset is discoverable, whether the exploit works, what safeguards stand in the way and whether the outcome has operational value for an attacker. That turns remediation from a patching race into focused risk reduction.
This approach also exposes gaps between security ownership teams. The route to compromise may cross a web development team, cloud operations, identity management and a third-party supplier. A credible attack path gives leadership an evidence-based reason to bring those teams together and assign clear ownership.
For technology vendors serving the UK market, this is commercially relevant as well as technically useful. Buyers are increasingly sceptical of tools that create more alerts without helping them decide what matters. A proposition that demonstrates exploitability, validates controls and guides action is easier for a reseller to position with a security-conscious customer.
External penetration testing is not the same as continuous validation
A conventional penetration test is valuable, but it is a point-in-time exercise. The external attack surface changes constantly as teams launch applications, alter cloud permissions, add SaaS services, onboard suppliers and make emergency configuration changes. A test completed in April cannot validate an exposure introduced in May.
That does not make annual or project-based testing redundant. It means organisations should be clear about the question they need answered. A scoped penetration test is particularly effective before a major launch, after a material infrastructure change, during supplier assurance or when leaders need a deep assessment of a high-value application.
Continuous adversarial exposure validation addresses a different operational need. Rather than simply cataloguing vulnerabilities, it continually checks external exposures from an attacker’s perspective to establish what can genuinely be exploited. This reduces the noise created by theoretical findings and keeps pace with a changing perimeter.
Armory Defence’s AEV platform is positioned around that validation model. It helps teams focus on exploitable exposure paths rather than treating every discovered weakness as equally urgent. For organisations with fast-moving cloud estates or frequent application releases, that is a useful complement to targeted human-led testing.
What a credible engagement should include
The quality of an external penetration test depends heavily on scope, methodology and reporting. A cheap assessment that checks a narrow set of known ports and returns automated scan output will not reveal much about real attacker behaviour. Equally, an open-ended test without agreed rules can create avoidable risk for production services.
A strong engagement starts by defining the business objective. Is the priority to test an internet-facing customer portal, verify a newly exposed remote access service, assess a merger-related estate or establish an external security baseline? The answer determines the assets, depth and testing approach.
The assessment should normally cover four connected stages:
- Reconnaissance to identify the true external footprint, including overlooked domains, services and technology stacks.
- Vulnerability analysis and manual validation to separate exploitable weaknesses from scanner noise.
- Controlled exploitation to demonstrate the feasible attack path and its potential impact within agreed boundaries.
- A practical report that explains the evidence, remediation actions, ownership and retesting requirements.
Manual testing is particularly important for web applications, identity flows and misconfigurations. Automated tools are excellent at coverage and speed, but they cannot reliably judge business logic flaws or determine whether several modest findings become a serious route to compromise.
Rules of engagement protect the business and the test
The term penetration testing can sound aggressive, but a professional engagement is tightly governed. Before testing begins, both parties should agree the authorised targets, permitted testing windows, prohibited actions, escalation contacts and treatment of sensitive data.
This is where trade-offs need to be explicit. Testing production systems provides the most realistic answer, but it requires safeguards to avoid service disruption. Social engineering, denial-of-service testing and data exfiltration simulations may be relevant to a mature programme, yet they are not always necessary to validate an external attack path. The right scope is the one that answers the security question without taking unnecessary operational risk.
Organisations should also clarify whether the test is black box, grey box or white box. Black-box testing provides the closest representation of an external attacker with no internal knowledge. Grey-box access can increase efficiency and help validate specific concerns. White-box testing offers the deepest technical coverage, but it is less representative of initial attacker reconnaissance. None is universally best.
How to turn findings into measurable improvement
The report should be the start of the work, not the finish. Security leaders need a remediation plan that distinguishes urgent attack paths from hardening opportunities and records the business owner for each action. A useful finding explains the affected asset, attack narrative, evidence, impact, recommended fix and method for retesting.
Retesting matters because a closed ticket is not proof that the route has been removed. A change may fix one vulnerable component while leaving the exposed service, weak permission or alternate path intact. Independent validation confirms whether remediation has worked in the environment attackers can actually reach.
There is also a valuable detection opportunity. Where a controlled test demonstrates reconnaissance, credential use or lateral movement, the security team can check whether its EDR, XDR, NDR and identity controls generated meaningful alerts. Prevention is the first objective, but detection and response capability determine how much damage can occur if prevention fails.
Building a stronger market conversation around exposure
For cyber security vendors and channel partners, external exposure is a practical route into senior security conversations. It connects technical capability to a concern boards understand: whether an attacker can get in and what happens if they do. The strongest message is not that a product produces more findings. It is that it helps teams identify exploitable paths, prioritise remediation and prove that their defences work.
That requires disciplined positioning. External penetration testing, adversarial exposure validation and detection technologies overlap in outcome, but they do not do the same job. A clear channel strategy explains where each capability fits, when it should be deployed and why the customer should act now rather than wait for a breach to expose the gap.
The most useful next step is simple: take one high-value internet-facing service and ask whether the business can prove its real attack paths are understood, remediated and continuously checked. If the answer is uncertain, that is where focused testing should begin.